
INTRODUCTION
How much exploitation can one operator manage at once? On 31 August a likely Russian-speaking actor began using hundreds of AI agents to develop, test and run a chain against two PaperCut NG/MF flaws, reaching at least 440 instances across 395 organizations in 48 countries. At full tilt the campaign compromised 11 organizations in 26 seconds. GreyNoise also watched it stall, with multi-day gaps between initial access and follow-on activity, purely because the human behind it did not follow up.
Proofpoint watched four espionage clusters pick up the same BlueMoon exploit kit inside two weeks, most of them with a suspected China nexus, chaining two Chromium bugs with a Windows kernel escalation. Cisco Talos separately documented three unrelated clusters inside Secure Firewall Management Center, one stealing credentials through a web shell, one tied to Sandworm and dropping Cyclops Blink, and one assessed as a Qilin-linked ransomware operator.
What links them is not AI, and it is not zero-days. It is reuse. One operator reused an exploit chain across hundreds of PaperCut targets. Four crews reused one browser kit rather than each funding their own research. Three unrelated groups reused the authority already pooled inside a single firewall manager.
The expensive work gets done once and then applied in as many places as it will fit. The question that follows is uncomfortable and worth asking anyway. Where has your environment concentrated enough trust that one working technique would suddenly scale?
Get The Monday Brief in your inbox every Monday. Subscribe for free, and share it with someone who’d find it useful.
Thanks for supporting The Monday Brief.
WEEKLY SIGNALS ANALYSIS
One operator can now run far more exploitation in parallel than one operator used to manage. Hundreds of agents drove the PaperCut chain to 11 organizations in 26 seconds at peak, then stalled for days whenever the human still had to act.
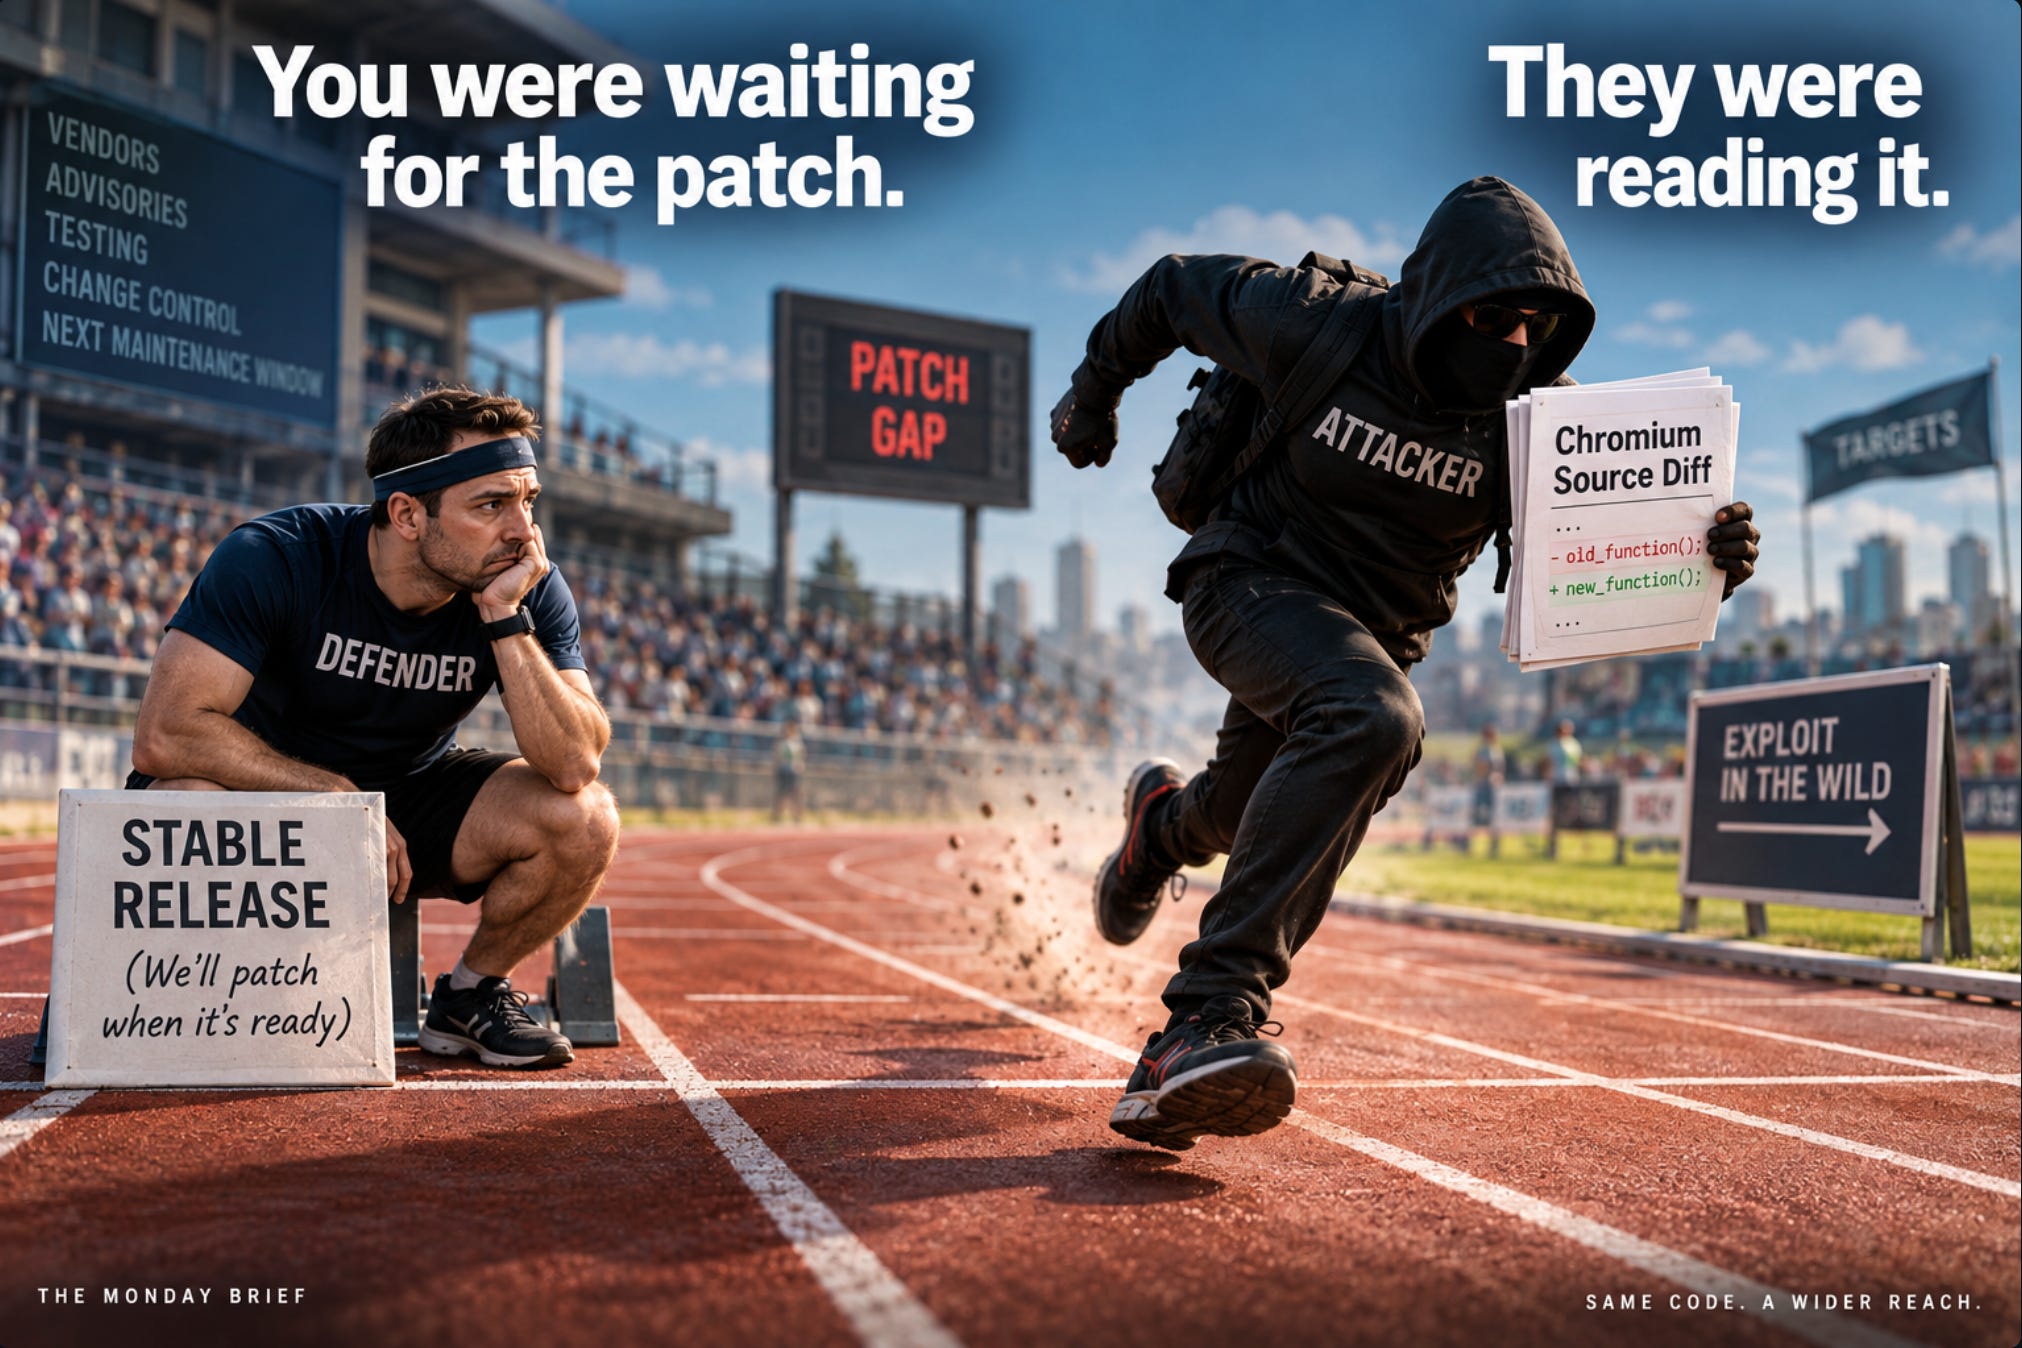
The window between a public upstream fix and a shipped browser update is now attack surface. Four espionage clusters adopted BlueMoon within two weeks, chaining two Chromium flaws with a Windows kernel escalation. Chromium patches land in public source before stable Chrome reaches users, which hands an attacker a working diff.
Firewall management infrastructure is a target in its own right. Talos documented three unrelated clusters inside Cisco FMC, one taking credentials, one tied to Sandworm delivering Cyclops Blink, and one assessed with high confidence as a Qilin-linked ransomware operator. Three operators, one platform, no coordination between them.
AI services are becoming operational tooling for attackers and a target worth attacking. Anthropic documented a Russia-linked actor whose agents rebuilt its malware until security products stopped flagging it. A separate crew spent four days on roughly 30 AI companies chasing a pre-release Claude model, never reached it, and the keys it took were customer keys lifted from a third-party vendor's environment.
What not to over-index on: raw CVE counts. Microsoft shipped a record 974 fixes this week and two of them are under active exploitation. Working down a scanner’s critical list in order spends the hours that the PaperCut and FMC campaigns show you may not have.
Signal 1: AI Agents Ran the PaperCut Exploitation Campaign, Compromising 395 Organizations
Why it matters: Beginning 31 August, a likely Russian-speaking actor used hundreds of AI agents to develop, test and run a chain against two flaws in PaperCut NG/MF, print management software that tracks and controls print jobs across office and school networks. GreyNoise ties the campaign to at least 440 compromised instances at 395 organizations across 48 countries, with credentials taken from 280 victims and administrator privileges reached at 12. At peak it compromised 11 organizations in 26 seconds.
What is being misread: Coverage frames this as AI-powered attacks, which invites you to imagine novel malware. There is none. Automated exploitation has existed for decades, and the agents here ran an OpenAI Codex harness, a DeepSeek model and ordinary offensive tooling against targets they enumerated through Netlas, an internet-wide search service. What changed is how much of the repetitive work ran at once. It did not remove the operator, and the same report shows intrusions sitting idle for days because nobody followed up.
Think Red (Douglas McKee): Automated exploitation is old news. Scanners, fuzzers and exploit frameworks have been chewing through this problem since long before anyone said agentic. What is worth looking at is how much of the loop ran concurrently. Build the chain, test it, pick targets, retry the failures, and keep several hundred of those going at the same time. That is a throughput change, not a capability change. And the honest part of the GreyNoise write-up is the stalling. Access sat untouched for days in places because the operator never came back to it, which tells me the machine was handling the fan-out while a person was still deciding what any of it was worth. I still need to run that second half by hand. It does not get faster because the first half did.
Act Blue (Ismael Valenzuela): I have been saying for years that attackers are lazy. If something easy works, why change it? What agents change is how far easy stretches. From target discovery to initial access, this operator observed, oriented, decided and acted at agent speed, one working chain reaching 440 instances while most defensive processes still cycle on a weekly cadence. Defenders need to start operationalizing defense at machine speed too, because an architecture is only defensible if it holds at that tempo. PaperCut has replaced the emergency patches with maintenance releases, so the first job is confirming exposed instances are actually on the fixed build rather than trusting the change ticket. Any instance reachable from 27 August onward deserves a look for unfamiliar administrative accounts, unexpected processes, credential access and outbound connections the business cannot explain, because these flaws were exploited as zero-days before this campaign launched and credentials came out of 280 victims once it did. We argued exposure-based prioritization after the JFrog chaining, and what this adds is speed on the attacker's side. Anything in that estate without a real reason to face the internet should come off it, and whatever stays needs the instrumentation you would give a tier-one asset.
Supporting sources:
Help Net Security: AI agents compromised at least 440 PaperCut instances across 395 organizations
The Hacker News: Attacker used hundreds of AI agents to compromise 440+ PaperCut instances
SecurityWeek: Russian threat actor used AI to build, test, and deploy exploits at scale
The Hacker News: PaperCut replaces emergency patches with fixes for two actively exploited flaws
Arctic Wolf: URGENT UPDATE: Active Exploitation of Two Chained PaperCut NG/MF Vulnerabilities CVE-2026-81578 and CVE-2026-82078
Signal 2: Four Espionage Crews Adopted the Same Browser Exploit Kit Inside Two Weeks
Why it matters: Proofpoint attributes the first in-the-wild use of a kit it calls BlueMoon to the China-aligned actor TA412, also tracked as APT31, on 28 August. Within days three more espionage clusters were using it, most of them with a suspected China nexus. The chain pairs a V8 remote code execution bug and a sandbox escape in Chromium with a Windows kernel privilege escalation, and it reached NGOs, aerospace, manufacturing and government targets. Capability moved between crews faster than any one of them could have built it.
What is being misread: Four groups on one kit looks like sloppy tradecraft and is closer to the opposite. The part worth understanding is where the Chromium bugs came from. Fixes land in public Chromium source before they reach a stable Chrome build, so the diff is readable to anyone willing to reverse it, and the exploit can exist before the update does. That is a narrower and more useful claim than saying patching stopped working. These vulnerabilities are fixed now. The exposure was the interval, and a reusable kit meant four crews could work inside it at once.
Think Red (Douglas McKee): The mechanic worth studying here is the patch gap. Finding a browser bug from scratch is expensive. Reading a public commit that fixes one is not, and in an open codebase the fix is visible before the product carrying it ships. That turns someone else’s remediation into a specification. Every security vendor I have worked for does this to build protections as fast as possible. Threat actors can package the result so it runs from a single script and the same window is suddenly being worked by several unrelated crews rather than one. The defender in that interval is not slow. There is simply nothing available to install yet, which is a different problem from a maintenance window nobody kept to.
Act Blue (Ismael Valenzuela): A browser zero-day removes one preventive control for a period of weeks, and a defensible architecture is built on the assumption that any single control can fail. The rest of the intrusion does not become invisible, and that is where the work goes. Prioritize browser processes launching command interpreters or other unexpected children, then persistence and privilege escalation on the endpoints that matter, and correlate those rather than alerting on each in isolation. For the people handling diplomatic, defense or engineering material, reduce what a compromised browser can reach in the first hop. Segmentation and browser isolation are worth the friction for that group specifically, because they are the controls that still apply while the vendor update does not exist.
Supporting sources:
BleepingComputer: BlueMoon kit exploited Windows and Chrome zero-day flaws across multiple espionage groups
CyberScoop: Chinese espionage groups swarm to exploit triple-link chain of zero-days
CSO Online: Attackers weaponize the gap between Chromium fixes and Chrome patches
Signal 3: Three Unrelated Clusters Exploited Cisco Firewall Managers for Very Different Ends
Why it matters: Cisco Talos is tracking three distinct clusters exploiting Secure Firewall Management Center, and their objectives barely overlap. UAT-12197 used CVE-2026-20079 to drop a web shell and a malicious JAR that harvested authentication data. UAT-11823, which Talos ties to the Russian actor Sandworm, exploited both flaws and delivered the Cyclops Blink implant. UAT-11988 is assessed with high confidence as a ransomware operator connected to Qilin. The first flaw, CVE-2026-20079, is an authentication bypass carrying a CVSS score of 10.0 and yielding root on the underlying system. The second, CVE-2026-20316, is a static credential issue that permits login through a low-privileged account, and it is the one the Qilin-linked cluster used to get in.
What is being misread: Filed as another critical CVE, this loses what the three clusters actually show. FMC concentrates administrative authority, configuration detail and a map of what the estate trusts, so reaching it offers something an ordinary server does not. Talos saw that position used for credential theft, reconnaissance, tunneling and persistence, by groups with nothing else in common. The architectural question is where your evidence about the FMC comes from. If the console is monitored only through telemetry it generates and network paths its own firewalls control, then whoever reaches it also controls the record of their own intrusion. It is the camera room problem. Every feed in the building runs through one room, and no camera points at the room itself.
Think Red (Douglas McKee): Security management systems get filed mentally as controls rather than as targets, and that is the habit worth breaking. What I would want from an FMC is not some magic switch that opens every firewall. It is the credentials, configuration, the shape of the estate, which segments talk to which. That is reconnaissance I would otherwise spend weeks assembling, sitting in one place, on a box that is supposed to be authoritative. Three groups with unrelated goals all found it worth their time in the same window, which says more about the value of that position than any one of their payloads does.
Act Blue (Ismael Valenzuela): We often talk about zero trust for users and workloads, but the management plane usually gets a pass. These campaigns show what that pass costs. A CVSS 10.0 authentication bypass that yields root argues for patching before anything else on the list, but note that the Qilin-linked cluster never touched it. They logged in with static credentials tied to the second flaw, CVE-2026-20316, so closing the bypass without rotating those credentials leaves the ransomware path open. After that, restrict the management interface to a dedicated administrative path rather than leaving it broadly reachable, so a credential stolen anywhere in the estate does not land you on the console. Where a manager was exposed before remediation, work from the indicators Talos published instead of assuming compromise, because three clusters means three different sets of artifacts to look for. The control that outlasts both CVEs is no camera room without a camera on it. Administrative sessions, configuration changes, credential access and unexpected outbound connections need to land somewhere the FMC itself cannot rewrite, because a security platform should not be the only witness to its own compromise.
Supporting sources:
Cisco Talos: Technical report separating UAT-12197, UAT-11823 tied to Sandworm, and the Qilin-linked UAT-11988, with indicators
The Hacker News: Cisco FMC flaws exploited to steal credentials and deploy Qilin ransomware
BleepingComputer: Cisco FMC flaws exploited by ransomware gang and state-sponsored hackers
Signal 4: A Russia-Linked Actor Used Claude to Rebuild Malware Until Detections Stopped Firing
Why it matters: Anthropic disrupted an actor it tracks as GTG-20006, working across more than 20 organizations including government ministries, defense and intelligence bodies, embassies and defense-industrial firms concentrated in Ukraine and Europe. Its agents watched security products flag the actor's own implants, then rebuilt the malware autonomously until the detections stopped. A separate crew hit roughly 30 AI companies inside four days looking for API keys and a pre-release Claude model. Every path to that model failed, Anthropic says its own systems were not compromised, and the keys that were taken were customer keys lifted from a third-party vendor's environment.
What is being misread: The headline reads as AI makes attackers smarter, and the national cyber director put it better this week when he said AI is surfacing long-standing problems rather than inventing new ones. Malware evasion is not new. The shift is that detection became an input to development rather than the end of it. It is also worth saying plainly that this particular actor was not a small crew leveling up. Anthropic describes tradecraft consistent with Midnight Blizzard, which is a mature state-backed program automating work it could already do.
Think Red (Douglas McKee): Malware authors have been testing payloads against defenses and filing down whatever gets caught for as long as defenses have existed. We even teach this at SANS. What changed here is that the loop closed. Detection fires, that result feeds back into development, the code changes, the test runs again, and none of it waits on somebody noticing in the morning. That does not remove the operator who knows what the objective is or what the target environment looks like. It makes the iteration cheap enough to run continuously, which is exactly where anyone should expect this technology to show up first.
Act Blue (Ismael Valenzuela): A rebuild loop aimed at your detections automates away the bottom of the Pyramid of Pain, where the indicators that cost the attacker nothing to change live. Hashes and signatures now regenerate in minutes, so weight what the payload still has to do once it works. It has to obtain credentials, persist, reach outward and use an identity against something else, and those behaviors survive a recompile in a way a file hash does not. The second case is the agent identity problem I wrote about for SANS back in June, showing up in the wild. Anthropic was never compromised, and customer API keys were still stolen, lifted from a third-party vendor's environment where customers had placed them. Model-provider keys are non-human identities, so inventory where yours actually live, including inside vendors and tooling you did not build, and treat them as production credentials with rotation and scope to match.
Supporting sources:
The Record: Anthropic caught Russia-linked spies using Claude in hacking operations against 20+ organizations
CyberScoop: AI lets small actors run state-level hacking campaigns, Anthropic report finds
SecurityWeek: Anthropic says Russian hackers used Claude to automate malware evasion, criminals targeted vendor infrastructure
CyberScoop: National cyber director says AI surfaced long-standing issues rather than creating new ones
SANS Institute (Ismael Valenzuela): The Agent Identity Problem, the zero trust framing for non-human identities referenced in Act Blue
ROLE-BASED TAKEAWAYS
Executive / CISO / Board Level
Exposure outranks severity score in deciding what gets patched first. The PaperCut campaign moved through internet-facing instances faster than a severity-ordered queue can work. Ask your security team how quickly they could contain an actively exploited internet-facing service, and how long their tooling takes to produce a validated list of exposed instances after an advisory.
Your exposure to AI services is mostly your own credentials, not the provider’s security. The keys taken in this week’s campaign against AI companies were customer keys lifted from a third-party vendor’s environment. Request an inventory of which AI providers are in use and where their API credentials live, including keys placed with vendors and tooling your teams did not build.
Your security infrastructure can become part of the attack path. The Cisco FMC intrusions put three separate operators inside the console that configures the estate. Require independent monitoring and change control on the management planes of security products.
Enterprise Architect
Design Principle Impact: The management plane must be treated as a distinct trust tier, not part of the infrastructure it manages. The Cisco FMC intrusions show that a compromised control console grants estate-wide reach, so isolate management interfaces and monitor them independently of the devices they govern.
New Constraint/Dependency: AI services introduce a new external trust relationship covering data, API credentials and workflow availability. Threat-model misuse of your own AI integrations alongside theft of provider credentials from your environment and from third parties holding them, and constrain which enterprise data, secrets and privileges those services can reach.
Security Operations
Implementation Watch Item: For PaperCut NG/MF instances exposed from 27 August onward, review for unfamiliar administrative accounts, unexpected processes, credential access and outbound connections that no business process explains, and keep doing so after the maintenance release is applied.
Common Failure Mode: Treating this week’s record 974 Microsoft CVEs as the priority list and burning your limited hours there, while the two actively exploited flaws and the exposed edge apps go unaddressed. One of those two is the Windows kernel bug in the BlueMoon chain, which is the argument in one line.
Monitoring Patterns: For BlueMoon-style activity, prioritize browser processes launching command interpreters or other unexpected children, followed by persistence or privilege escalation. On FMC, correlate unexpected administrative sessions, credential access, configuration changes and outbound connections against the approved change record rather than alerting on any one of them alone.
Signal vs Noise Guidance: A genuine indicator is privileged action or lateral movement from a management console or edge appliance that no change ticket or business workflow explains. Routine scanner noise against an internet-facing service, with no follow-on execution behind it, is not post-compromise behavior.
Adversarial edge item: Scale creates repetition. Shared exploit kits and automated campaigns may reach more targets, but they also repeat process trees, network behavior, tooling, and post-exploitation patterns across victims. Build detections around those stable behaviors instead of the actor name or a single IOC that will change after the first report.
See you next Monday!
The Monday Brief is produced by Douglas McKee and Ismael Valenzuela. The opinions expressed are our own and do not reflect those of our employers.